TB
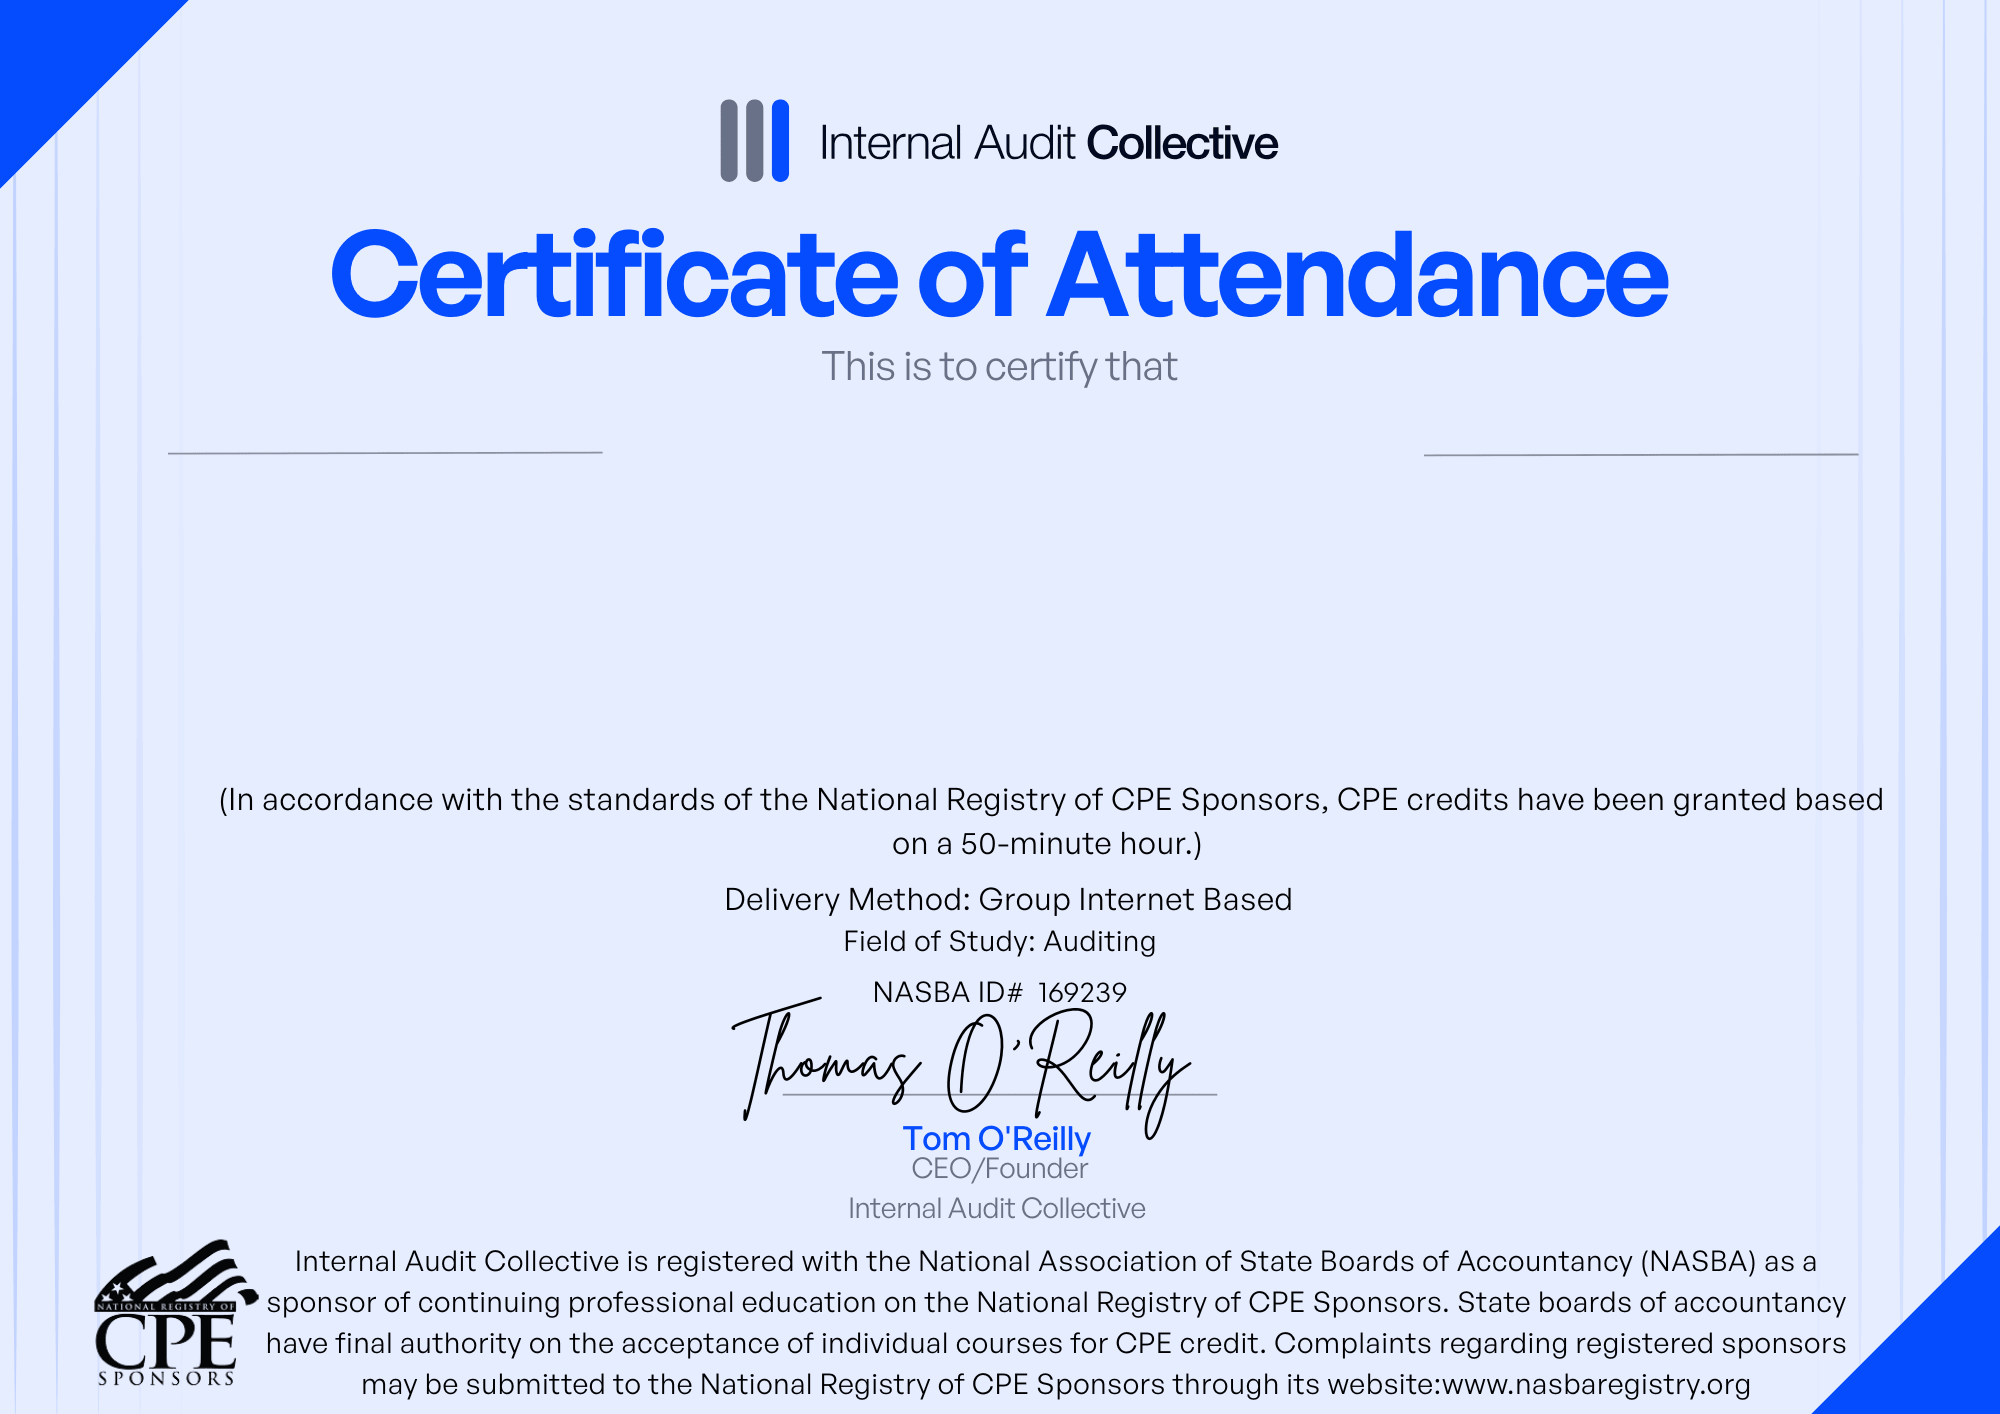
Issued to
Thomas Boyle
Want to report a typo or a mistake?
Credential Verification
Issue date: October 29, 2026
ID: 163be08a-13d6-4db7-b616-5d883ddfa37a
Type
Webinar
Level
Introductory
Format
Online
Duration
60 minutes
Price
Free
Description
The cybersecurity control frameworks most organizations rely on—NIST CSF, ISO 27001, CIS Controls, COBIT—were built for a threat landscape that no longer exists.
As AI accelerates the speed, scale, and sophistication of cyberattacks, Internal Audit's traditional approach to risk assessment, audit coverage, controls testing, and monitoring cadence is falling behind.
This session introduces an Adaptive Risk framework that helps Internal Audit teams recalibrate their methodology to keep pace with AI-augmented threats—shifting from static, backward-looking assurance to a dynamic model that flexes with the organization's actual risk exposure in real time.
The target audience for this webinar is any Internal Audit, Risk, or SOX professional with responsibilities or oversight for IT Audit, Cyber audit, or providing assurance or advice over their organization's use of AI.
Learning Objectives:
After completing this session, participants will be able to:
Identify threat-driven metrics that Internal Audit can monitor to trigger risk-informed adjustments to audit coverage when predefined thresholds are breached.
Define Adaptive Audit Priorities that direct audit activities toward the domains of greatest cybersecurity risk to the organization.
Design work programs that enable audit teams to perform hardened control testing—testing built to confirm controls can withstand an AI-driven threat environment.
Develop Audit Committee and Executive Leadership reporting that delivers forward-looking assurance rather than backward-looking compliance confirmation.
Skills
Auditing
Related documents